DATE
Loading...
TIME
Loading...
About Us
The Department of Information and Communications Technology (DICT) has confirmed that one of its “staging websites” was defaced, prompting an investigation into possible security vulnerabilities and unauthorized access.
In a statement, the DICT clarified that the affected website was a development and testing environment, not the final version intended for official public use.
The incident came after a threat actor identified as “4HMDOS4” claimed responsibility for the defacement, which displayed a message criticizing government spending, transparency, procurement, and restrictions imposed in the name of public safety.
According to a post by cybersecurity watch dog Deep Web Konek, the defaced page displayed a message demanding greater public oversight of DICT projects and government spending.
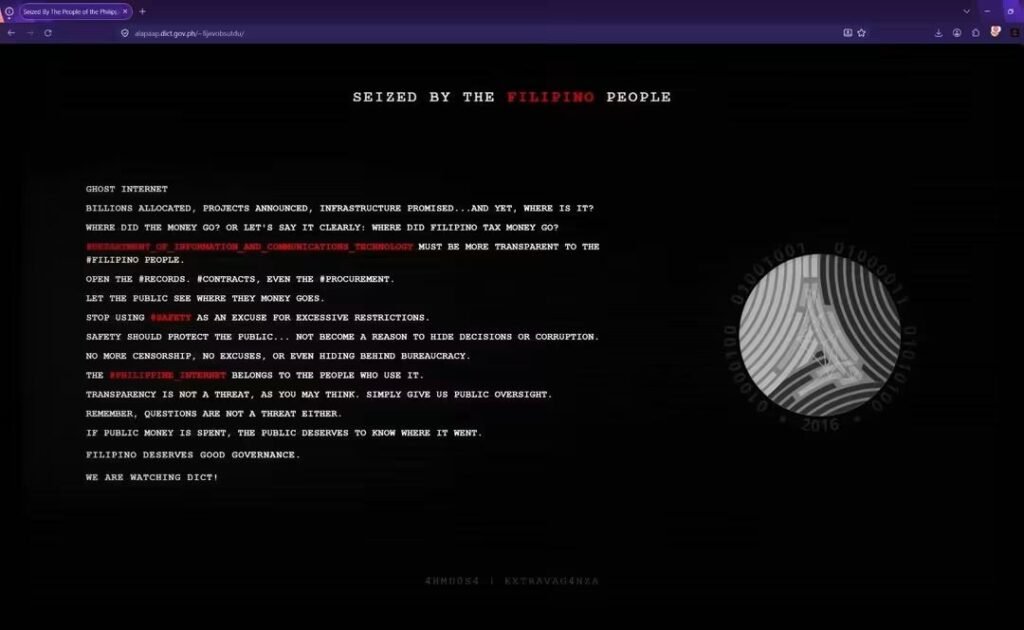
The unauthorized page carried the headline “SEIZED BY THE FILIPINO PEOPLE” and raised questions about the government’s internet infrastructure projects, including the allocation of public funds.
The message also called for greater transparency in government contracts and procurement, while criticizing censorship and restrictions justified on public safety grounds.
Screenshots of the incident showed the defaced website displaying the message against a black background, alongside a modified government emblem.
DICT launches security assessment
Following the incident, the DICT said it immediately initiated an assessment of the affected environment to determine the circumstances surrounding the unauthorized access and identify possible security weaknesses.
The department explained that the staging website was being used to evaluate functionality, configurations, and other components before its eventual deployment.
It is now reviewing the environment for vulnerabilities that may require remediation.
The findings will guide the implementation of corrective measures and improvements to the website’s security controls before it is deployed for official public use.
As a precaution, the DICT said all necessary security checks and validation activities must be completed before any related system becomes publicly accessible.
The department reiterated its commitment to strengthening the security of its digital infrastructure through testing, validation, and assessment before deploying its systems.