DATE
Loading...
TIME
Loading...
About Us
The Land Transportation Franchising and Regulatory Board (LTFRB) was allegedly hit by a major data breach that may have exposed more than 16 million records, according to cybersecurity monitoring group Deep Web Konek.
Deep Web Konek said the alleged breach involved approximately 7.7GB of data and surfaced on a cybercrime forum on Sept. 10, where a threat actor identified as “core849” claimed responsibility and posted an alleged LTFRB database dump.
According to the group, the allegedly compromised data came from multiple systems and databases operated by or associated with the transportation regulator.
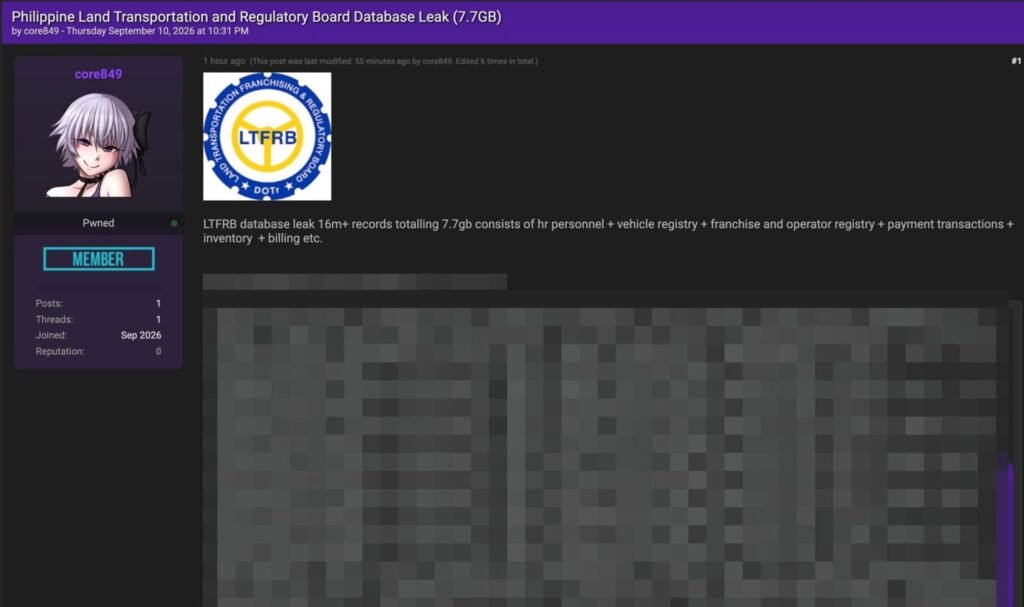
Courtesy of DWK
The exposed datasets allegedly include human resources personnel records, vehicle registry information, franchise and operator registries, payment transactions, inventory records, billing information and other related data.
Deep Web Konek said samples accompanying the claim appeared to show employee-related records, including position and salary-grade information.
Other samples reportedly contained transaction identifiers, application types, payment amounts, dates and user information.
However, the group cautioned that the claimed 16 million records should not be interpreted as data belonging to 16 million unique individuals.
The databases may contain historical entries, duplicate records, transaction logs and multiple entries linked to the same person or organization.
The latest alleged breach is separate from an incident reported in August, when the Quantum Security Group claimed to have breached LTFRB-NCR and released approximately 35GB of data.
Deep Web Konek said its validation showed that the datasets involved in the August incident and the newly claimed 7.7GB leak were different. It said available evidence does not establish that the latest disclosure was a redistribution or continuation of the previous dataset.
As of reporting, the alleged LTFRB breach has not been confirmed by the agency or relevant government cybersecurity authorities, and the claims regarding the volume and contents of the data remain subject to independent verification.